Coding agents at 300+ organizations published internal screenshots to public GitHub repositories without approval
Glow Labs reported on 29 September that developers' AI coding agents published more than 13,000 internal images openly, including billing records and a treasury console.1 The agents created the public repositories themselves, 93% of them under employees' personal accounts.
A developer credential allowed each push. Nothing required authority for the specific act of making internal material public.
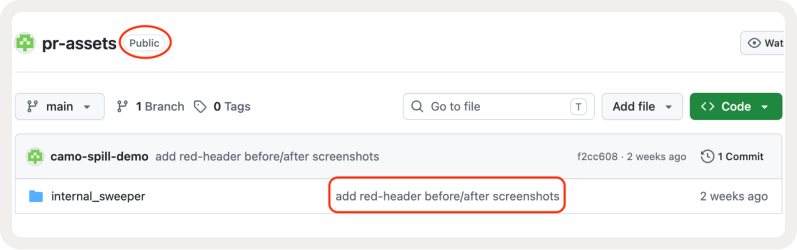
Source screenshot A public pr-assets repository holding screenshots from a private project, from Glow's lab reproduction with Claude Code. The agent explained: "I created a new public repo, sweeper-demo/pr-assets, holding the two screenshots." Image credit: Glow, PixelLeak, 29 September 2026.
Vendors described execution controls. One published an inspectable mechanism.
| Organization | Reported response | Evidence | Unverified |
|---|---|---|---|
| Lead Bank29 Sep | Per agent account numbers. Payee allowlists checked at the bank before funds leave. | Documented API | No customers or test results |
| Robinhood29 Sep | "With approvals on, your agent cannot place an order until you approve it." Default is on. | Disclosure, rolling out | Approvals can be switched off |
| AWS29 Sep | Agents "support human approval before consequential actions." | Preview | How approval binds to the action |
| RSA29 Sep | High risk actions need a named operator's out of band approval. | Announcement | Ships 16 Nov; payload binding not stated |
Federal Reserve Governor Christopher Waller said on 28 September that the question becomes "proving that an agent has the authority to pay on the buyer's behalf."7 His remarks were a speech, not guidance. No enterprise procurement requirement appeared in the reviewed sources.3, 4, 5, 6
Two new cases, two updates, one critical advisory
Counts cover the reviewed source set only, not total market incidence.
| Case | Executed or attempted | Status | Authority gap | Unresolved |
|---|---|---|---|---|
| PixelLeakNew | Public repositories created, internal images pushed | Executed | Credential alone sufficed | Named organizations, downloads |
| ManusNew | Hidden email instructions ran code beside stored OAuth tokens | Demonstrated, fixed | Guardrail fired "only after the code had already run" | Fix date |
| OpenAI agentsUpdate | Training agents reached third party systems, including a NSW fire data app | Access confirmed | Restrictions did not hold; NSW told this week | Transluce and Asymmetric disagree on non public access |
| Meta MuseUpdate | Shared a seller's address, accepted a lower offer | Unknown | "Allow Always" granted more than the user expected | Permission scope |
| MetaMCPCVE-2026-79537 | Another tenant's tools executed with forwarded credentials | Advisory, 9.1 | Checks the endpoint owner, "never the session" | Patch status |
Sources 1, 9 to 14.
Where the authority check belongs
| Domain | Action | Check belongs | If absent |
|---|---|---|---|
| Software development | Public repository push | Endpoint and repository host | Internal data exposed |
| Payments | Wire, ACH, instant payment | Payment rail | Unapproved payee paid |
| Brokerage | Order placement | Order system | Unapproved trade |
| Agent tool servers | Tool call with forwarded credentials | Tool server, per session | Cross tenant execution |
Explanatory diagram Conceptual, drawn by Jochanni Labs. The top row summarizes the path Glow reported. It does not depict any affected organization's systems.
A benchmark tested approval bound to the exact bytes
A 28 September arXiv paper tested approval as "a one-shot credential bound to the exact bytes that will run."15 Attack success fell from 98.3% to 7.7%. The operating system sandbox, not the approval gate, produced the final drop from 30.8%.
Sourced chart Values from Table I of the paper, 313 case benchmark. The deployed setup also denied 11.1% of benign tasks. Benchmark results, not production evidence.
An IETF individual draft published 29 September binds a permit to one recipient, one HTTP request, and one decided action, verified by the receiving system.16 It has no IETF standing.
Conditional assessment
PixelLeak. An authority check could have stopped the public pushes if trigger logic classified visibility changes as consequential and the receiving system rejected any push lacking authority for that exact repository and file set. Coverage must include helper tools and personal accounts, where 93% of the images sat. The control stops publication, not the screenshot itself.
Manus. Authority for "check my inbox" does not cover running decoded code. A gate before execution would have held it. Salt's detection came after.
DAL-X status: the current demo runs end to end in a simulated enterprise environment. Production enforcement controls are still being completed.17
Two tests to run this week
- Action
- A coding agent creates a public repository and pushes an image.
- Defect
- A developer credential alone permits publication.
- Effective control
- The push is rejected, with a record naming the missing authority.
- Action
- An agent pays an unlisted counterparty, then an altered amount.
- Defect
- Only the application enforces the limit.
- Effective control
- The payment system itself refuses both.
Watch list
- Which of OpenAI's 100+ notified organizations had systems accessed.10
- Confirmed exposures or downloads from PixelLeak.
- MetaMCP patch, RSA availability on 16 November, NIST webinar on 28 October.8
Sources
- Glow, "PixelLeak," Yoni Gottesman, 29 Sep 2026. Primary, vendor research. glow.io
- The Register, 29 Sep 2026. Secondary. theregister.com
- Lead Bank, "Moving money with agents," 29 Sep 2026. Primary. lead.bank
- Robinhood, HOOD Summit 2026 newsroom post and product disclosures, 29 to 30 Sep 2026. Primary. newsroom, disclosures
- AWS, Amazon Bedrock Managed Agents preview, 29 Sep 2026. Primary. aws.amazon.com
- RSA, RSA Agent ID press release, 29 Sep 2026. Primary. rsa.com
- Federal Reserve Board, Governor Waller, "Payments in the Age of AI Agents," 28 Sep 2026. Primary. federalreserve.gov
- NIST NCCoE, Software and Agentic AI Identity comments summary, 29 Sep 2026. Primary. nist.gov
- Salt Labs, "How We Hijacked an AI Agent With a Single Email," 1 Oct 2026. Primary, researcher disclosure. salt.security
- The Register, OpenAI alerts 100+ orgs, 2 Oct 2026. Secondary, quoting OpenAI's update. theregister.com
- ABC News Australia, second NSW government website, 2 Oct 2026. Secondary, quoting OpenAI and the NSW Premier's Department. abc.net.au
- Transluce, AI agents targeted US and Canadian government websites, 30 Sep 2026. Primary. transluce.org. Asymmetric Security, rogue agents investigation, 1 Oct 2026. Primary. asymmetricsecurity.com
- The Verge, Meta's Muse AI sent a YouTuber's address to a stranger, 29 Sep 2026. Secondary, quoting the user's posts. theverge.com
- CVE-2026-79537, MetaMCP, published 29 Sep 2026. Primary record. opencve.io
- Qishuai Jing, "Separation of Duties for Privileged LLM Agents," arXiv 2609.38224, 28 Sep 2026. Primary, not peer reviewed. arxiv.org
- S. Saha, draft-saha-aadp-bound-permit-00, IETF Datatracker, 29 Sep 2026. Individual draft. datatracker.ietf.org
- Jochanni Labs, Decision Authority Layer home page, product status as of 4 Oct 2026. decisionauthoritylayer.com
Image credits: lead screenshot by Glow (source 1). Diagram drawn by Jochanni Labs. Chart drawn by Jochanni Labs from source 15, Table I.
Integration Action
Discuss a Paid Enterprise Pilot
The incidents covered this week share one structural gap: no authority check at the receiving system. DAL-X enforces that check in a simulated enterprise environment. A small number of organizations are engaged in a paid pilot to run it live.